Dependabot Can Update AI Agent Skills. Who Reviews What Changed?
Dependabot can propose version updates for agent dependencies. The change puts skills and instructions into an existing review workflow.
12 articles
Dependabot can propose version updates for agent dependencies. The change puts skills and instructions into an existing review workflow.
An internal DeepSeek evaluation separates exploit capability from operational restraint. Define scope, evidence and cleanup before autonomous testing.
EMBRACE is a useful reminder that an embedded browser does not automatically keep the security boundaries of a standalone browser.
Turn AI security benchmark claims into a scoped evaluation with reproducible findings, reviewed patches and deployment retests.
Cloudflare’s open-source coding-agent skill uses coverage-led hunting, independent validation, and structured evidence. Here is what the workflow can—and cannot—establish.
AI can help analysts navigate compiled software, but a decompiler output is not a vulnerability report. See how REA changes analysis, why reverse- engineering agents need protection, and how teams can validate findings.
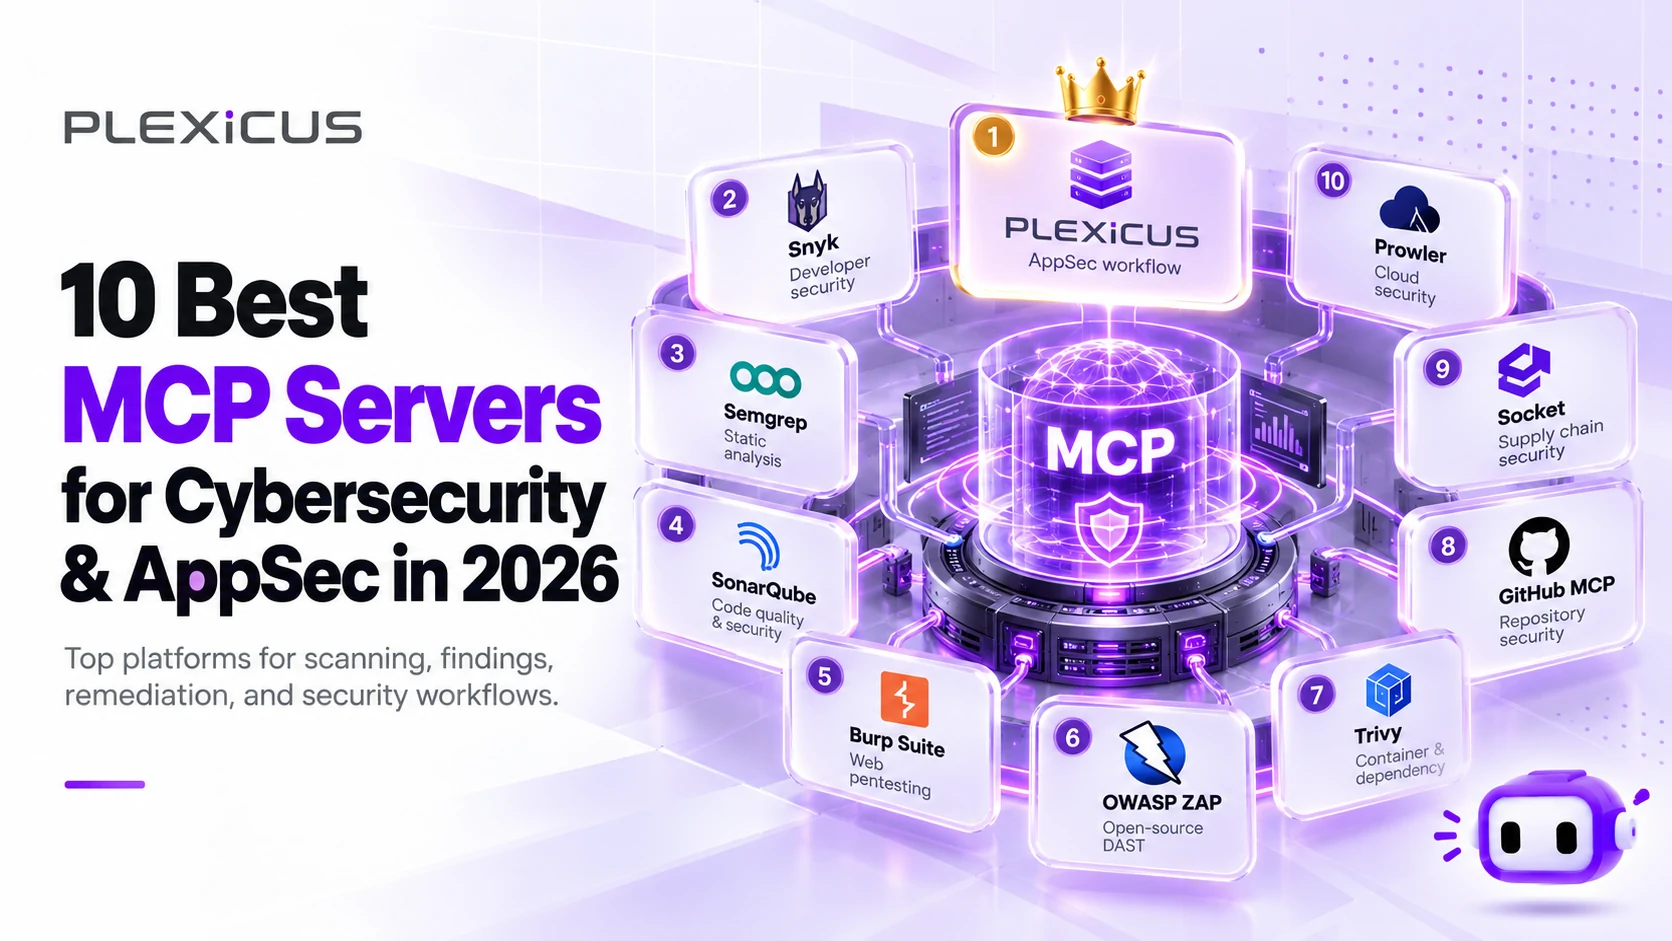
An editorial guide to security MCP integrations for AI-assisted development: repository findings, scanning, web testing, supply chain analysis, and cloud security.
A fruit-fly connectome offers a vivid test of a security principle: a demo is not proof until controls show what the advertised system contributes.
DevDay 2026 connected persistent agents, cloud coding, plugins, events, and shared work. Here is what shipped, what is still coming, and where AppSec boundaries lie.
Opus 5.5 motion-graphics demos reveal an agentic loop: plan, write code, run it, inspect, revise. Claude cybersecurity now depends on verification keeping pace.
Jev AI returns typed decisions instead of prose. That could change where semantic judgment fits in security workflows, if teams keep policy, fallbacks, verification, and human review.
AI can remove repetitive AppSec work without removing accountability. Learn how to decide what to automate, what to augment, and when a security decision should be escalated to a person.
Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.